API Mode Integration
@rootauth/core is the framework-free RootAuth SDK. It handles configuration, encryption, authentication requests, MFA, third-party login, session operations, and language switching, but does not render UI.
Preparation
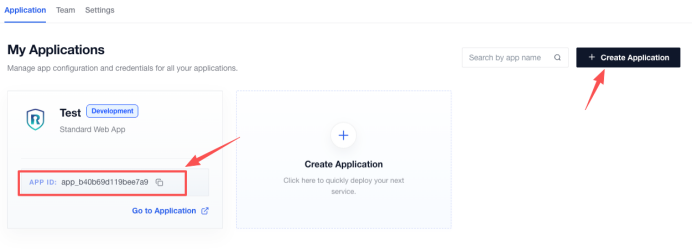
Create an application in the RootAuth Console and copy the app_id (format: app_******).
Please add the following configuration line to the .npmrc file in the project root directory:
@rootauth:registry=http://gitlab.standard-software.co/api/v4/projects/12421/packages/npm/1. Installation
@rootauth/core is the UI-free base SDK for RootAuth authentication APIs, request configuration, sessions, and shared utilities. This section shows installation with npm.
npm install @rootauth/core2. Create a client
The client stores shared options such as app_id, API URL, OIDC parameters, and locale. This section covers client creation, required options, and the complete configuration table.
import { RootAuthClient, type RootAuthClientConfig } from '@rootauth/core'

const config: RootAuthClientConfig = {
  app_id: 'your-app-id',
  api_base_url: 'https://rootauth-api.rootauth.com',
  redirect_uri: window.location.origin,
  scope: ['openid'],
  cloudflare_container: '#rootauth-turnstile',
})

const rootAuth = new RootAuthClient(config)

// Optional: preload and cache app config and the device fingerprint.
await rootAuth.install()
An install() preload failure does not block application startup. If it is omitted or the preload fails, login() and register() fetch the required data before submitting.
2.1 Configuration
| Option | Type | Required | Default | Description |
|---|---|---|---|---|
app_id |
string |
Yes | None | Application ID created in the RootAuth console |
api_base_url |
string |
No | https://rootauth-api.rootauth.com |
API base URL |
redirect_uri |
string |
No | window.location.origin |
OIDC callback URL after login or registration |
scope |
string[] |
No | ['openid'] |
Requested user-field scope |
state |
string |
No | undefined |
Custom state returned unchanged in the callback |
grant_type |
string |
No | authorization_code |
OIDC authorization mode |
locale |
string |
No | zh-CN |
Supports zh-CN and en-US |
enable_google_one_tap |
boolean |
No | false |
Allows googleOneTapLogin() to start Google One Tap |
cloudflare_container |
string |
Yes with Cloudflare | undefined |
Dedicated container CSS selector used by every Turnstile mode |
3. Calling convention
Authentication methods return promises and selected flows also accept an onSuccess callback. Supplying the callback transfers success handling to the application, while failures throw normalized error objects.
Authentication methods return a Promise and accept an optional onSuccess callback:
interface RootAuthFlowCallbacks<T> {
  onSuccess?: (response: T) => void
}
When onSuccess is supplied, login and registration do not perform the SDK default redirect or automatic login; the application handles the result.
The following interfaces support this callback convention: sendCode(), login(), verifyLoginMfa(), register(), resetPassword(), and updateProfile().
const result = await rootAuth.login({
  type: 'EMAIL_PASS',
  email: 'user@example.com',
  password: 'password',
})rootAuth.login(
{
type: 'EMAIL_PASS',
email: 'user@example.com',
password: 'password',
},
{
onSuccess(result) {
console.log(result)
},
}
)Successful responses and errors may carry an SDK message:
interface RootAuthMessage {
  type: string
  msg: string
}

interface RootAuthMessageCarrier {
  rootauth_message?: RootAuthMessage
}
type is one of success, warning or error, msg is the final localized copy returned by the backend for the current locale.
Core renders no UI. The application must display messages from rootauth_message or error objects.
4. Login: login()
login() supports email, phone, username, verification-code, WhatsApp, and invitation login flows. This section lists every type, its authentication method, required fields, and examples.
4.1 Complete type list
type |
Login method | Required account fields | Credential field |
|---|---|---|---|
EMAIL_PASS |
Email and password | email |
password |
EMAIL_CODE |
Email and verification code | email |
code |
PHONE_PASS |
Phone and password | phone_code, phone_num |
password |
PHONE_CODE |
Phone and verification code | phone_code, phone_num |
code |
USER_NAME_PASS |
Username and password | user_name |
password |
WHATSAPP_CODE |
WhatsApp verification code | phone_code, phone_num |
code |
4.2 Parameters
| Parameter | Type | Default | Description |
|---|---|---|---|
type |
Login type above | None | Required login method |
email |
string |
None | Required for email types |
phone_code |
string |
PHONE_PASS, PHONE_CODE, WHATSAPP_CODE |
Calling code without +, for example 86 |
phone_num |
string |
PHONE_PASS, PHONE_CODE, WHATSAPP_CODE |
Phone number without the calling code |
user_name |
string |
None | Required for username login |
password |
string |
Password types | Plaintext input; encrypted with the application RSA public key |
code |
string | number |
Verification-code types | Six-digit verification code |
is_invite |
number |
EMAIL_PASS, EMAIL_CODE |
Whether this is an invitation registration login |
redirect_uri |
string |
Client configuration | Overrides the configured redirect URI |
scope |
string[] |
Client configuration | Overrides configured scopes |
state |
string |
Client configuration | Overrides configured OIDC state |
grant_type |
string |
Client configuration | Overrides configured grant type |
The caller must pass the correct type; the SDK does not infer the login method from supplied fields. When MFA follows login, loginAccountType is derived from this explicit login type. A TOTP account name is then selected from the matching account field: email for email login, phone for phone login, and username for username login.
await rootAuth.login({
  type: 'PHONE_CODE',
  phone_code: '86',
  phone_num: '13800000000',
  code: '123456',
})
5. Send a code: sendCode()
sendCode() sends codes for login, registration, password reset, and MFA flows. This section describes email, SMS, WhatsApp, and other type values with their required parameters.
If the error message Too many incorrect verification code attempts. Please request a new code. appears when requesting a verification code, go to Console > General Security > CAPTCHA Rules > CAPTCHA Attempt Count to check whether the configured limit meets your requirements.
5.1 Complete type list
type |
Verification method | Required fields |
|---|---|---|
EMAIL |
Email code | email, email_template_type |
PHONE_TEXT |
SMS code | phone_code, phone_num, phone_text_template_type |
WHATSAPP |
WhatsApp code | phone_code, phone_num |
5.2 email_template_type and phone_text_template_type values
| Template value | Purpose |
|---|---|
register_code |
Registration code |
login_code |
Login code |
reset_pass_code |
Password-reset code |
login_mfa_code |
MFA login code; also requires mfa_token |
5.3 Parameters
| Parameter | Type | Required condition | Description |
|---|---|---|---|
type |
string |
Always | EMAIL, PHONE_TEXT, or WHATSAPP |
email |
string |
type = EMAIL |
Email address |
email_template_type |
string |
EMAIL |
register_code, login_code, reset_pass_code, or login_mfa_code |
phone_code |
string |
PHONE_TEXT, WHATSAPP |
Calling code without +, for example 86 |
phone_num |
string |
type = PHONE_TEXT/WHATSAPP |
Full phone number without the calling code |
phone_text_template_type |
string |
PHONE_TEXT |
register_code, login_code, reset_pass_code, or login_mfa_code |
mfa_token |
string |
Template is login_mfa_code |
MFA token returned by the login endpoint |
ticket |
string |
CAPTCHA is enabled and supplied by the app | Tencent CAPTCHA ticket; the SDK flow overwrites it when applicable |
ticket_rand_str |
string |
CAPTCHA is enabled and supplied by the app | Random string paired with the Tencent CAPTCHA ticket |
redirect_uri |
string |
Optional | Overrides the configured redirect URI |
scope |
string[] |
Optional | Overrides the configured scopes |
state |
string |
Optional | Overrides the configured state |
grant_type |
string |
Optional | Overrides the configured grant type |
device_id |
string |
Optional | Device fingerprint; the SDK may generate one when omitted |
email_template_type is used only with EMAIL, and phone_text_template_type only with PHONE_TEXT. WHATSAPP does not use a template parameter.
await rootAuth.sendCode({
  type: 'EMAIL',
  email: 'user@example.com',
  email_template_type: 'register_code',
})await rootAuth.sendCode({
type: 'PHONE_TEXT',
phone_code: '86',
phone_num: '13800000000',
phone_text_template_type: 'login_code',
})When CAPTCHA is enabled, the SDK runs Tencent CAPTCHA automatically. The business UI controls delivery frequency and the 60-second countdown.
6. Registration: register()
register() supports email, phone, username, and WhatsApp registration. This section lists registration type values, required fields, and complete code-registration calls.
6.1 Complete type list
type |
Registration method | Required fields |
|---|---|---|
EMAIL_CODE_PASS |
Email code and password | email, code, password |
PHONE_CODE_PASS |
Phone code and password | phone_code, phone_num, code, password |
USER_NAME_PASS |
Username and password | user_name, password |
WHATSAPP_CODE |
WhatsApp verification-code registration | phone_code, phone_num, code |
6.2 Parameters
| Parameter | Type | Required condition | Description |
|---|---|---|---|
type |
string |
Always | Registration type listed above |
email |
string |
EMAIL_PASS, EMAIL_CODE |
Email address |
phone_code |
string |
PHONE_CODE_PASS, PHONE_CODE, WHATSAPP_CODE |
Calling code without + |
phone_num |
string |
PHONE_CODE_PASS, PHONE_CODE, WHATSAPP_CODE |
Phone number without calling code |
user_name |
string |
USER_NAME_PASS |
Username |
code |
string | number |
EMAIL_CODE, PHONE_CODE, WHATSAPP_CODE |
Verification code |
password |
string |
EMAIL_PASS, PHONE_CODE_PASS, USER_NAME_PASS |
Plaintext; encrypted by the SDK |
redirect_uri |
string |
Optional | Overrides the client redirect URI |
scope |
string[] |
Optional | Overrides the authorization scopes |
state |
string |
Optional | Overrides the state value |
grant_type |
string |
Optional | Overrides the grant type |
device_id |
string |
Optional | Device fingerprint |
await rootAuth.register({
  type: 'EMAIL_CODE_PASS',
  email: 'user@example.com',
  code: '123456',
  password: 'password',
})await rootAuth.register({
type: 'USER_NAME_PASS',
user_name: 'rootauth-user',
password: 'password',
})Passwords are encrypted with the application's RSA public key. Without onSuccess, the SDK may redirect based on the backend response or automatically log in when there is no redirect_url.
7. Reset password: resetPassword()
Password reset supports submitting a verification code directly or validating it first and then using the returned verify_token.
7.1 Verify code: verifyResetPasswordCode()
| Parameter | Type | Required condition | Description |
|---|---|---|---|
type |
string |
Always | EMAIL_CODE or PHONE_CODE |
email |
string |
EMAIL_CODE |
Email address |
phone_code |
string |
PHONE_CODE |
Calling code without + |
phone_num |
string |
PHONE_CODE |
Phone number without the calling code |
code |
number |
Always | Verification code |
const verification = await rootAuth.verifyResetPasswordCode({
  type: 'EMAIL_CODE',
  email: 'user@example.com',
  code: 123456,
})
The response data contains verify_token.
7.2 Reset password: resetPassword()
At least one of code and verify_token is required.
| Parameter | Type | Required condition | Description |
|---|---|---|---|
type |
string |
Always | EMAIL_CODE or PHONE_CODE |
email |
string |
EMAIL_CODE |
Email address |
phone_code |
string |
PHONE_CODE |
Calling code without + |
phone_num |
string |
PHONE_CODE |
Phone number without the calling code |
password |
string |
Always | New password |
password_confirmation |
string |
Always | Confirmation password |
code |
string | number |
Required without verify_token |
Verification code |
verify_token |
string |
Required without code |
Token returned by the code verification API |
redirect_uri, scope, state, grant_type |
Global config types | No | Override the global config for this request |
await rootAuth.resetPassword({
  type: 'EMAIL_CODE',
  email: 'user@example.com',
  verify_token: verification.data.data.verify_token,
  password: 'NewPassword123',
  password_confirmation: 'NewPassword123',
})
8. MFA: verifyLoginMfa()
verifyLoginMfa() handles email, phone, and TOTP verification as well as first-time binding. This section explains each mfa_type, code content, and additional fields.
mfa_type |
Verification method | code content |
Additional fields |
|---|---|---|---|
EMAIL |
Verify bound email | Email code | None |
EMAIL_BIND |
Bind and verify email | Email code | email |
PHONE_CODE |
Verify bound phone | SMS code | Usually the phone from the login response |
PHONE_CODE_BIND |
Bind and verify phone | SMS code | phone_code, phone_num |
TOTP |
Verify bound authenticator | Authenticator code | None |
TOTP_BIND |
Bind an authenticator for the first time | Authenticator code | totp_bind_code when totp_bind_need_verify_code=true |
8.1 Parameters
| Parameter | Type | Required condition | Description |
|---|---|---|---|
mfa_token |
string |
Always | MFA token returned by login |
mfa_type |
string |
Always | EMAIL, EMAIL_BIND, PHONE_CODE, PHONE_CODE_BIND, TOTP, or TOTP_BIND |
code |
string | number |
Always | Email, SMS, or TOTP code |
email |
string |
EMAIL_BIND |
Email to bind |
phone_code |
string |
PHONE_CODE_BIND |
Calling code without + |
phone_num |
string |
PHONE_CODE_BIND |
Phone number to bind |
totp_bind_code |
string |
TOTP_BIND with totp_bind_need_verify_code=true |
Code used to bind the authenticator |
await rootAuth.verifyLoginMfa({
  mfa_type: 'TOTP',
  code: '123456',
})
mfa_methods may contain multiple options. For TOTP_BIND, the login response may also contain totp_secret for QR-code generation.
9. Third-party login
Third-party authentication covers Google OAuth, Telegram, Facebook, VK, and WeChat Official Account QR flows. This section distinguishes redirects, Google One Tap, and QR polling, and clarifies that WhatsApp is not third-party OAuth.
9.1 thirdPartyLogin()
| Parameter | Type | Required condition | Description |
|---|---|---|---|
auth_by |
string |
Always | google_oauth, telegram, facebook, or vkid |
response_type |
string |
Optional | OAuth response type |
redirect_uri |
string |
Optional | Overrides the client redirect URI |
scope |
string[] |
Optional | Overrides the authorization scopes |
state |
string |
Optional | Overrides the state value |
grant_type |
string |
Optional | Overrides the grant type |
device_id |
string |
Optional | Device fingerprint |
auth_by |
Provider |
|---|---|
google_oauth |
Google OAuth |
telegram |
Telegram |
facebook |
|
vkid |
VK ID |
await rootAuth.thirdPartyLogin({
  auth_by: 'google_oauth',
})
thirdPartyLogin() is only for Google OAuth, Telegram, Facebook, and VK. It obtains the authorization URL and redirects to the page configured by redirect_uri.
WhatsApp is not a third-party OAuth provider; both WhatsApp login and registration use login() or register() with type: 'WHATSAPP_CODE'.
9.2 Google One Tap
const rootAuth = new RootAuthClient({
  app_id: 'your-app-id',
  enable_google_one_tap: true,
})

await rootAuth.googleOneTapLogin()
Google One Tap must be enabled in application configuration and requires Google's browser script and a valid client ID.
9.3 WeChat Official Account QR code
WeChat Official Account does not use thirdPartyLogin(). Call wechatServiceQrLogin() to obtain QR authorization data, then query the scan result with getThirdPartyQrResult() and the returned state_key.
const qr = await rootAuth.wechatServiceQrLogin()

const result = await rootAuth.getThirdPartyQrResult({
  state_key: qr.data.data.state_key,
})
Display qr.data.data.qr_url or authorize_url and use expire_seconds as the polling deadline. getThirdPartyQrResult() performs one query; the application must schedule polling and stop on success, expiry, or view disposal.
10. Session, configuration, and language
This section summarizes current-user lookup, logout, application configuration, and locale APIs. These supporting methods share the same Core client as login and registration.
| Method | Purpose |
|---|---|
getAppConfig() |
Fetch application login, registration, branding, agreement, and MFA settings |
getToken() |
Read the current access token |
isAuthenticated() |
Check whether the client has an access token |
logout() |
End the current session |
setAppId(appId) |
Change the application ID |
setLocale(locale) |
Switch request language |
await rootAuth.getAppConfig()
rootAuth.getToken()
rootAuth.isAuthenticated()
rootAuth.logout()
rootAuth.setAppId('another-app-id')
rootAuth.setLocale('en-US')
11. Related modes
Applications that do not build every authentication screen can use Web Components, Vue Hosted, or React Hosted. This section links each integration and explains its level of UI ownership.
@rootauth/web-components: standalone forms for any frontend stack.@rootauth/vue: complete hosted pages for Vue 3.@rootauth/react: complete hosted pages for React 18+.
;}.cls-2{fill:%230868f7;}.cls-3{fill:url(%23未命名的渐变_44);}.cls-4{fill:%23333;}%3c/style%3e%3clinearGradient%20id='未命名的渐变_8'%20x1='33.73'%20y1='100.61'%20x2='-0.03'%20y2='-1.06'%20gradientUnits='userSpaceOnUse'%3e%3cstop%20offset='0'%20stop-color='%237ae9fb'/%3e%3cstop%20offset='0.67'%20stop-color='%232b90f8'/%3e%3cstop%20offset='1'%20stop-color='%230868f7'/%3e%3c/linearGradient%3e%3clinearGradient%20id='未命名的渐变_44'%20x1='27.86'%20y1='18.67'%20x2='68.36'%20y2='22.22'%20gradientUnits='userSpaceOnUse'%3e%3cstop%20offset='0'%20stop-color='%235ac7f2'/%3e%3cstop%20offset='1'%20stop-color='%230868f7'/%3e%3c/linearGradient%3e%3c/defs%3e%3cpath%20class='cls-1'%20d='M29,28.74V81.91l-9.51-3.68v0L8.52,74A7.17,7.17,0,0,1,4,67.32V24.54A3.76,3.76,0,0,1,9.08,21Z'/%3e%3cpath%20class='cls-2'%20d='M68.09,78.07a13.15,13.15,0,0,1-17.9,12.06L29,81.91h0V28.74L50.19,37A13.17,13.17,0,0,0,68.08,25.3h0Z'/%3e%3cpath%20class='cls-3'%20d='M68.08,25.3a13.19,13.19,0,0,1-6.73,10.87A13.09,13.09,0,0,1,50.19,37L29,28.74V6A3.76,3.76,0,0,1,34.1,2.52l25.59,9.91A13.22,13.22,0,0,1,68.08,25.3Z'/%3e%3cpath%20class='cls-4'%20d='M129.06,81.76a4.33,4.33,0,0,1-3.19-1.31,4.4,4.4,0,0,1-1.31-3.24V56.86H97.65V77.21a4.36,4.36,0,0,1-1.35,3.2A4.68,4.68,0,0,1,93,81.76a4.32,4.32,0,0,1-3.19-1.31,4.37,4.37,0,0,1-1.32-3.24V27.27A4.58,4.58,0,0,1,89.83,24a4.59,4.59,0,0,1,7.82,3.27V48.15h26.91V27.27A4.58,4.58,0,0,1,125.91,24a4.59,4.59,0,0,1,7.82,3.27V77.21a4.37,4.37,0,0,1-1.36,3.2A4.65,4.65,0,0,1,129.06,81.76Z'/%3e%3cpath%20class='cls-4'%20d='M163.77,81.66c-6.57,0-11.76-1.92-15.44-5.7s-5.54-9.07-5.54-15.74a26.76,26.76,0,0,1,2.09-10.43,17.72,17.72,0,0,1,6.67-8.06,19.15,19.15,0,0,1,10.68-2.95,19,19,0,0,1,10.46,2.8,18.7,18.7,0,0,1,6.55,7.36,22.53,22.53,0,0,1,2.36,10.28A4.51,4.51,0,0,1,177,63.77H152.23a10.8,10.8,0,0,0,3.49,6.65c2,1.68,4.88,2.52,8.66,2.52a22.25,22.25,0,0,0,7.54-1.21c.74-.3,1.55-.67,2.37-1.07a3.75,3.75,0,0,1,1.84-.4,4.09,4.09,0,0,1,3,1.15,4,4,0,0,1,1.12,3,4.38,4.38,0,0,1-2.58,3.82,32.34,32.34,0,0,1-6.36,2.61A28.67,28.67,0,0,1,163.77,81.66ZM172.4,55.9a9.72,9.72,0,0,0-1.63-4.56A9.9,9.9,0,0,0,167,48a10.38,10.38,0,0,0-4.64-1.14,12,12,0,0,0-4.77,1.06,9.54,9.54,0,0,0-4.89,5.66,11.78,11.78,0,0,0-.51,2.3Z'/%3e%3cpath%20class='cls-4'%20d='M193,81.64a4.49,4.49,0,0,1-4.51-4.55V27.28A4.58,4.58,0,0,1,189.84,24a4.48,4.48,0,0,1,3.28-1.36A4.36,4.36,0,0,1,196.35,24a4.46,4.46,0,0,1,1.31,3.31V77.09a4.34,4.34,0,0,1-1.35,3.2A4.67,4.67,0,0,1,193,81.64Z'/%3e%3cpath%20class='cls-4'%20d='M263.79,81.71a5.7,5.7,0,0,1-4.2-1.74,5.76,5.76,0,0,1-1.73-4.19V27.37a4.58,4.58,0,0,1,1.35-3.27A4.59,4.59,0,0,1,267,27.37V72.53h24a4.58,4.58,0,0,1,3.27,7.82A4.66,4.66,0,0,1,291,81.71Z'/%3e%3cpath%20class='cls-4'%20d='M424.48,81.74a4.71,4.71,0,0,1-2.71-.88,5.43,5.43,0,0,1-1-1l-.07-.09-12.41-17-5.41,5v9.44a4.31,4.31,0,0,1-1.36,3.19,4.66,4.66,0,0,1-3.3,1.36A4.29,4.29,0,0,1,395,80.42a4.36,4.36,0,0,1-1.32-3.23V27.37A4.58,4.58,0,0,1,395,24.1a4.52,4.52,0,0,1,6.58.12,4.54,4.54,0,0,1,1.24,3.15V56.31l17.72-16.38.05,0a4.8,4.8,0,0,1,2.94-1.11,4.4,4.4,0,0,1,3.27,1.2,4.57,4.57,0,0,1,1.2,3.27,4.44,4.44,0,0,1-.77,2.33,7.45,7.45,0,0,1-1.43,1.65l-11,9.64,13.34,17.68a5,5,0,0,1,1,2.71,4.12,4.12,0,0,1-1.36,3.24A4.64,4.64,0,0,1,424.48,81.74Z'/%3e%3cpath%20class='cls-4'%20d='M317.93,81.76a21.5,21.5,0,1,1,21.17-21.5A21.37,21.37,0,0,1,317.93,81.76Zm0-34.1a12.61,12.61,0,1,0,12.42,12.6A12.52,12.52,0,0,0,317.93,47.66Z'/%3e%3cpath%20class='cls-4'%20d='M212.18,101.22a4.12,4.12,0,0,1-3.05-1.26,4.17,4.17,0,0,1-1.26-3.1V43.34a4.37,4.37,0,0,1,1.3-3.14,4.26,4.26,0,0,1,3.13-1.3,4.19,4.19,0,0,1,3.1,1.26,4.32,4.32,0,0,1,1.26,3.16,20.77,20.77,0,0,1,13-4.54,21.51,21.51,0,0,1,0,43,20.51,20.51,0,0,1-13-4.57V96.86a4.15,4.15,0,0,1-1.3,3.06A4.5,4.5,0,0,1,212.18,101.22Zm17.43-53.63c-6.23,0-12.93,4.11-12.93,12.72a12.73,12.73,0,0,0,25.46,0A12.71,12.71,0,0,0,229.61,47.59Z'/%3e%3cpath%20class='cls-4'%20d='M365.76,81.76a21.5,21.5,0,1,1,21.18-21.5A21.37,21.37,0,0,1,365.76,81.76Zm0-34.1a12.61,12.61,0,1,0,12.42,12.6A12.52,12.52,0,0,0,365.76,47.66Z'/%3e%3c/svg%3e)